JinjaCare
Solutions As you can see the title of the challenge, we will notice that this challenge is about SSTI, so let try ${7*'7'}} in any input form. But first, we need to register account. In Personal...
Solutions As you can see the title of the challenge, we will notice that this challenge is about SSTI, so let try ${7*'7'}} in any input form. But first, we need to register account. In Personal...
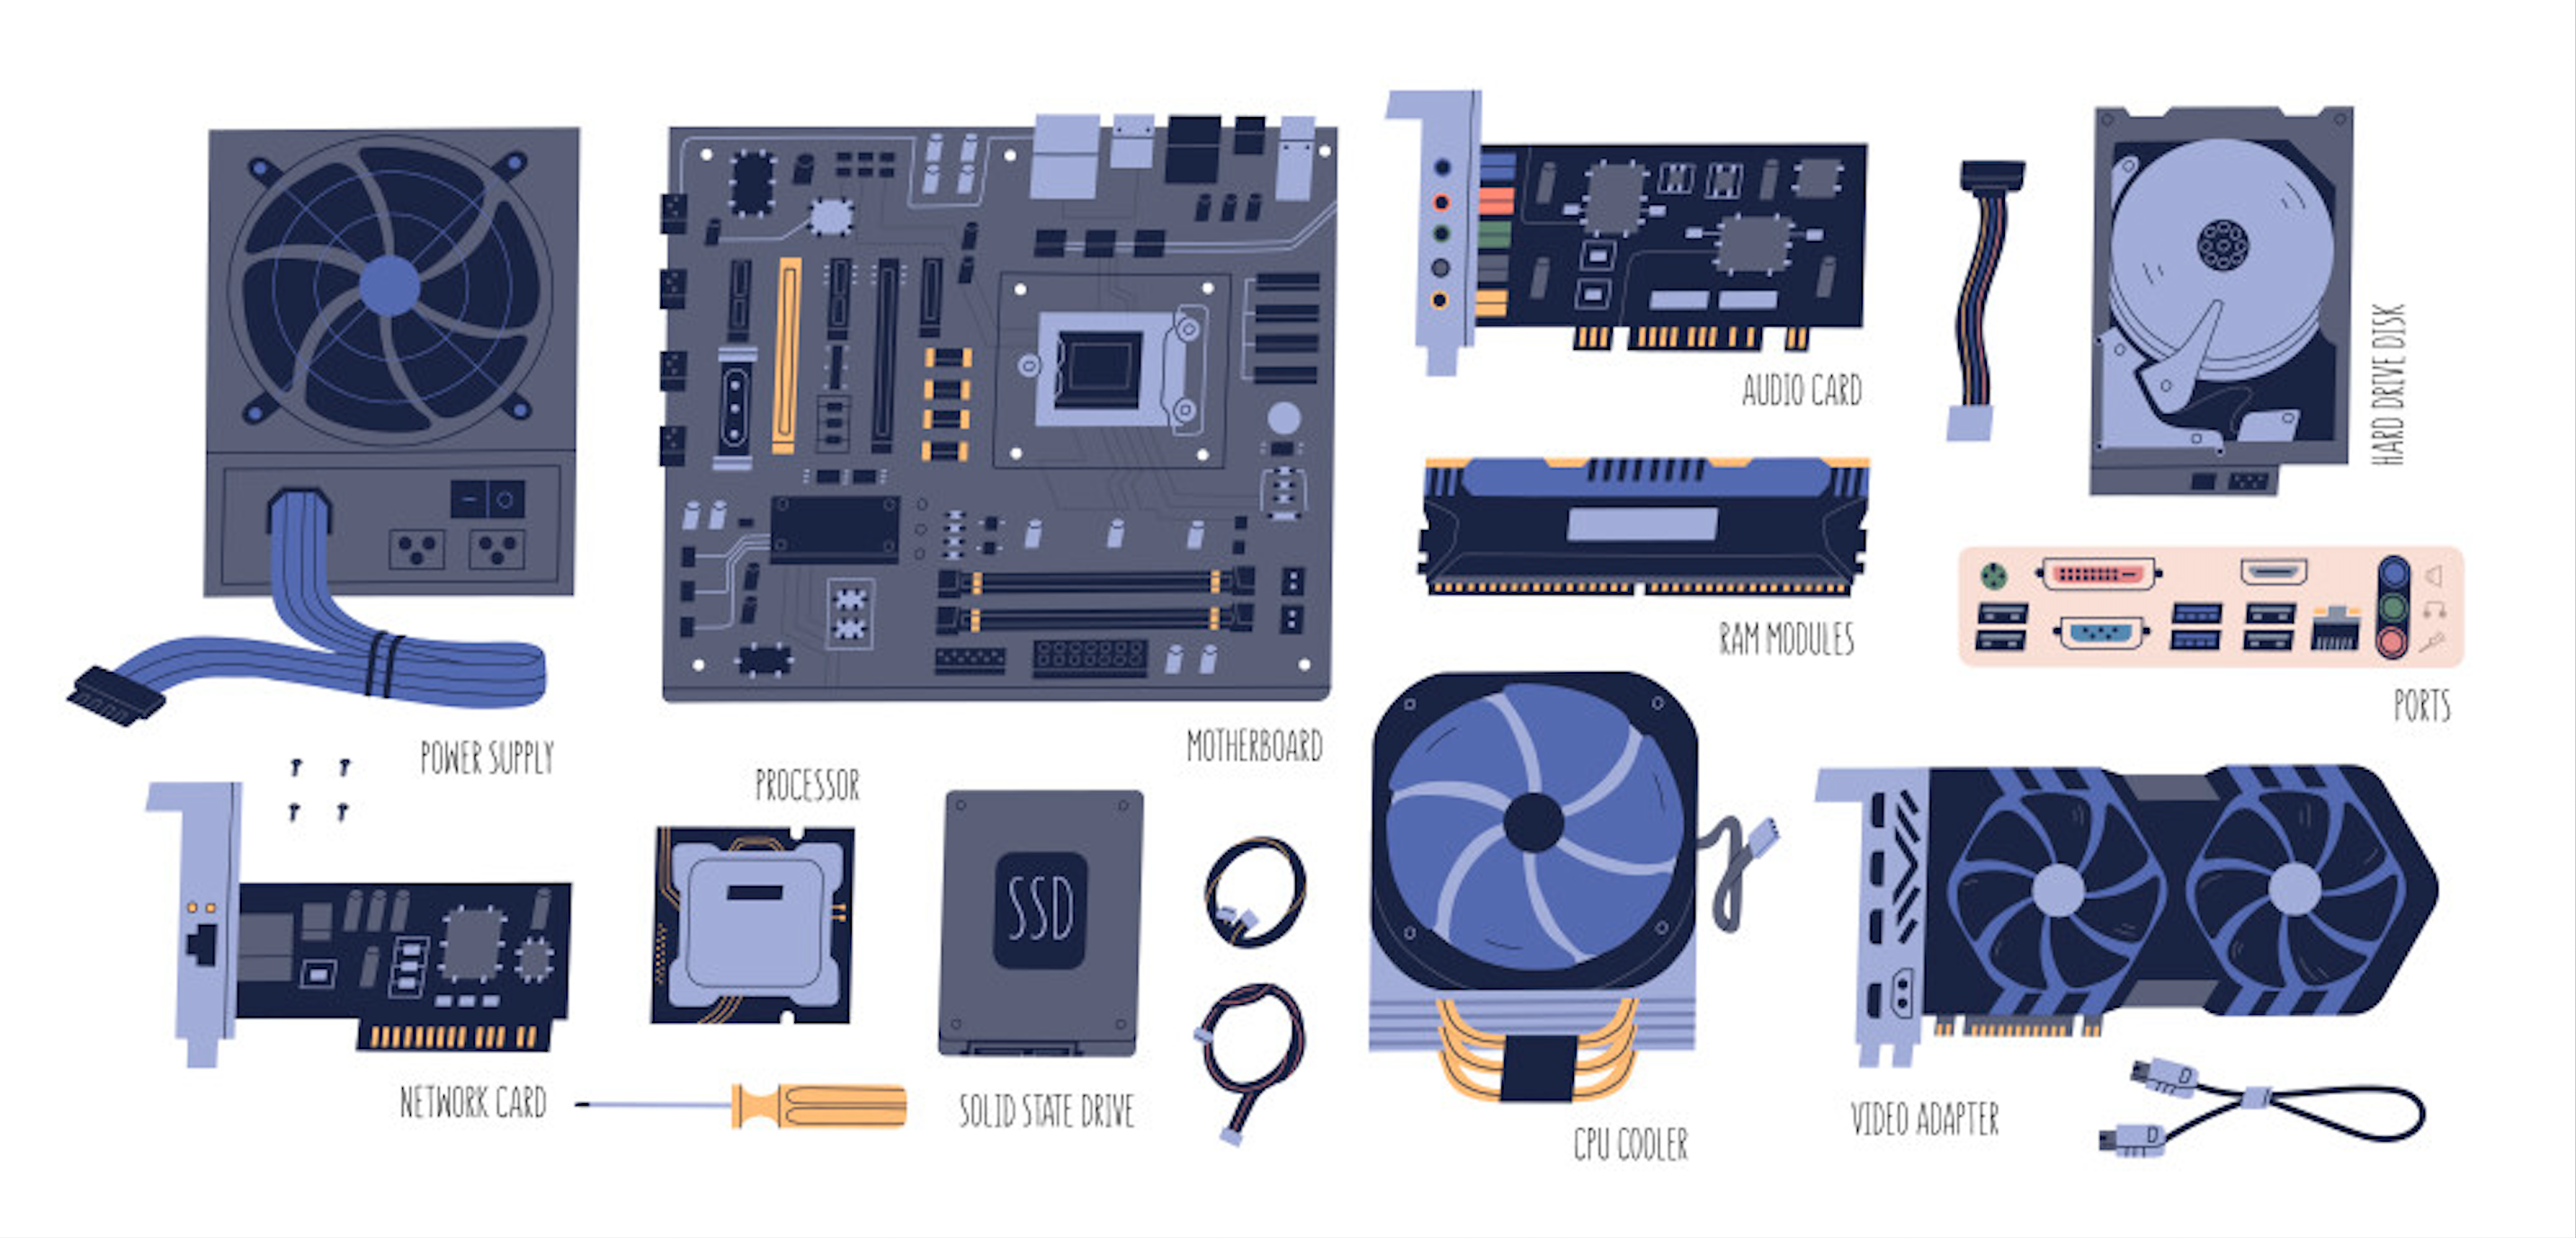
If you’re diving into cybersecurity, whether you dream of becoming a hacker, defender, or forensics wizard you need to understand the machine you’re working with. Before you start popping shells o...

So you have decided to dive into cybersecurity? Maybe you have heard about ethical hacking, Capture The Flag (CTF) challenges, or just want to break into tech in a fun and hands-on way. Good news:...

DDoS Mitigation Stack (Beginner Version) A beginner friendly, modular DDoS protection system using NGINX, Flask, ApacheBench, Firewall. Designed for learning, testing, and defending simple web app...
CHALLENGE DESCRIPTION Your boss is concerned about Volt Typhoon and some of their malware developments. He has requested that you obtain a copy of the associated malware and conduct a static analys...
DESCRIPTION A firmware update to a regional power grid controller was intercepted hours after the breach containment at the edge router. Task Force Phoenix believes this is the next phase of Opera...
DESCRIPTION Using credentials flagged in the previous investigation, Volnayan APTs have successfully breached a critical internal router. Telemetry from the affected systems indicates active latera...
DESCRIPTION After successfully leveraging a weak PIN system to access a critical internal server, you’ve infiltrated CygnusCorp’s network. Your next objective is clear: pivot laterally toward the ...
DESCRIPTION Following intel extracted from suspicious TOR traffic during Operation Blackout, you’ve uncovered a dump of leaked credentials linked to strategic user accounts. Advanced Persistent Thr...
DESCRIPTION After analyzing CygnusCorp’s leaked credentials, you successfully infiltrate a secondary layer of their internal network. During your investigation, you discover developer credentials t...